
Prove it. Don't just claim it.

Calling on Cyber Pros to Help Defend City Hall

Cybersecurity team reviewing a regional security update
Regional security update

Assess promptly

Government agencies with smaller budgets need support — and here's how you can help.

At a glance

  • Government agencies with smaller budgets need support — and here's how you can help.
  • SecurityTalent reviewed the linked official source and preserved its attribution.
Continue reading

Copyright

© SecurityTalent.com — original summary and analysis

  137 Hits
'Jewelbug' APT Balances State Espionage & Cryptocurrency Theft

Cybersecurity team reviewing a regional security update
Regional security update

Assess promptly

Researchers discovered hackers-for-hire performing cyber espionage and financially motivated heists from the same Web panel.

At a glance

  • Researchers discovered hackers-for-hire performing cyber espionage and financially motivated heists from the same Web panel.
  • SecurityTalent reviewed the linked official source and preserved its attribution.
Continue reading

Copyright

© SecurityTalent.com — original summary and analysis

  100 Hits

BdThemes Supply Chain Attack Poisons JSON to Create Rogue WordPress Admins

Cybersecurity team reviewing a regional security update
Regional security update

Assess promptly

Cybersecurity researchers have warned of a supply chain compromise impacting WordPress plugin vendor BdThemes, prompting the content management systems (CMS) platform's plugins team to temporarily disable their downloads. "Unlike traditional software supply chain attacks, zero source code files were modified within the official WordPress.org repository," Wordfence researcher Paolo Tresso said.

At a glance

  • Cybersecurity researchers have warned of a supply chain compromise impacting WordPress plugin vendor BdThemes, prompting the content management systems (CMS) platform's plugins team to temporarily disable their downloads. "Unlike traditional software supply chain attacks, zero source code files were modified within the official WordPress.org repository," Wordfence researcher Paolo Tresso said.
  • SecurityTalent reviewed the linked official source and preserved its attribution.
Continue reading

Copyright

© SecurityTalent.com — original summary and analysis

  86 Hits

15 TP-Link Bugs Expose Risks in Zero-Trust Provisioning

Cybersecurity team reviewing a regional security update
Regional security update

Assess promptly

Researchers are calling attention to the risks inherent in automated network device provisioning, using a world-leading device manufacturer as a case study.

At a glance

  • Researchers are calling attention to the risks inherent in automated network device provisioning, using a world-leading device manufacturer as a case study.
  • SecurityTalent reviewed the linked official source and preserved its attribution.
Continue reading

Copyright

© SecurityTalent.com — original summary and analysis

  102 Hits

Microsoft Bug Bounty Program: $20 Million Paid to 500 Researchers

Cybersecurity team reviewing a regional security update
Regional security update

Assess promptly

The biggest single reward paid out by Microsoft between July 1, 2025, and June 30, 2026, was $200,000. The post Microsoft Bug Bounty Program: $20 Million Paid to 500 Researchers appeared first on SecurityWeek.

At a glance

  • The biggest single reward paid out by Microsoft between July 1, 2025, and June 30, 2026, was $200,000. The post Microsoft Bug Bounty Program: $20 Million Paid to 500 Researchers appeared first on SecurityWeek.
  • SecurityTalent reviewed the linked official source and preserved its attribution.
Continue reading

Copyright

© SecurityTalent.com — original summary and analysis

  85 Hits

7 States’ Water Systems Hit by Cyberattacks Likely Tied to Iran

Cybersecurity team reviewing a regional security update
Regional security update

Assess promptly

Plus: The FBI eyes AI-powered tech to detect future crimes, Russia charges Telegram’s founder, xAI sues to stop a state’s “nudification” ban, and the Democrats learn a lesson about getting scammed.

At a glance

  • Plus: The FBI eyes AI-powered tech to detect future crimes, Russia charges Telegram’s founder, xAI sues to stop a state’s “nudification” ban, and the Democrats learn a lesson about getting scammed.
  • SecurityTalent reviewed the linked official source and preserved its attribution.

Copyright

© SecurityTalent.com — original summary and analysis

  70 Hits

NSA, CISA and International Partners Publish Coordinated Vulnerability Disclosure Guidance

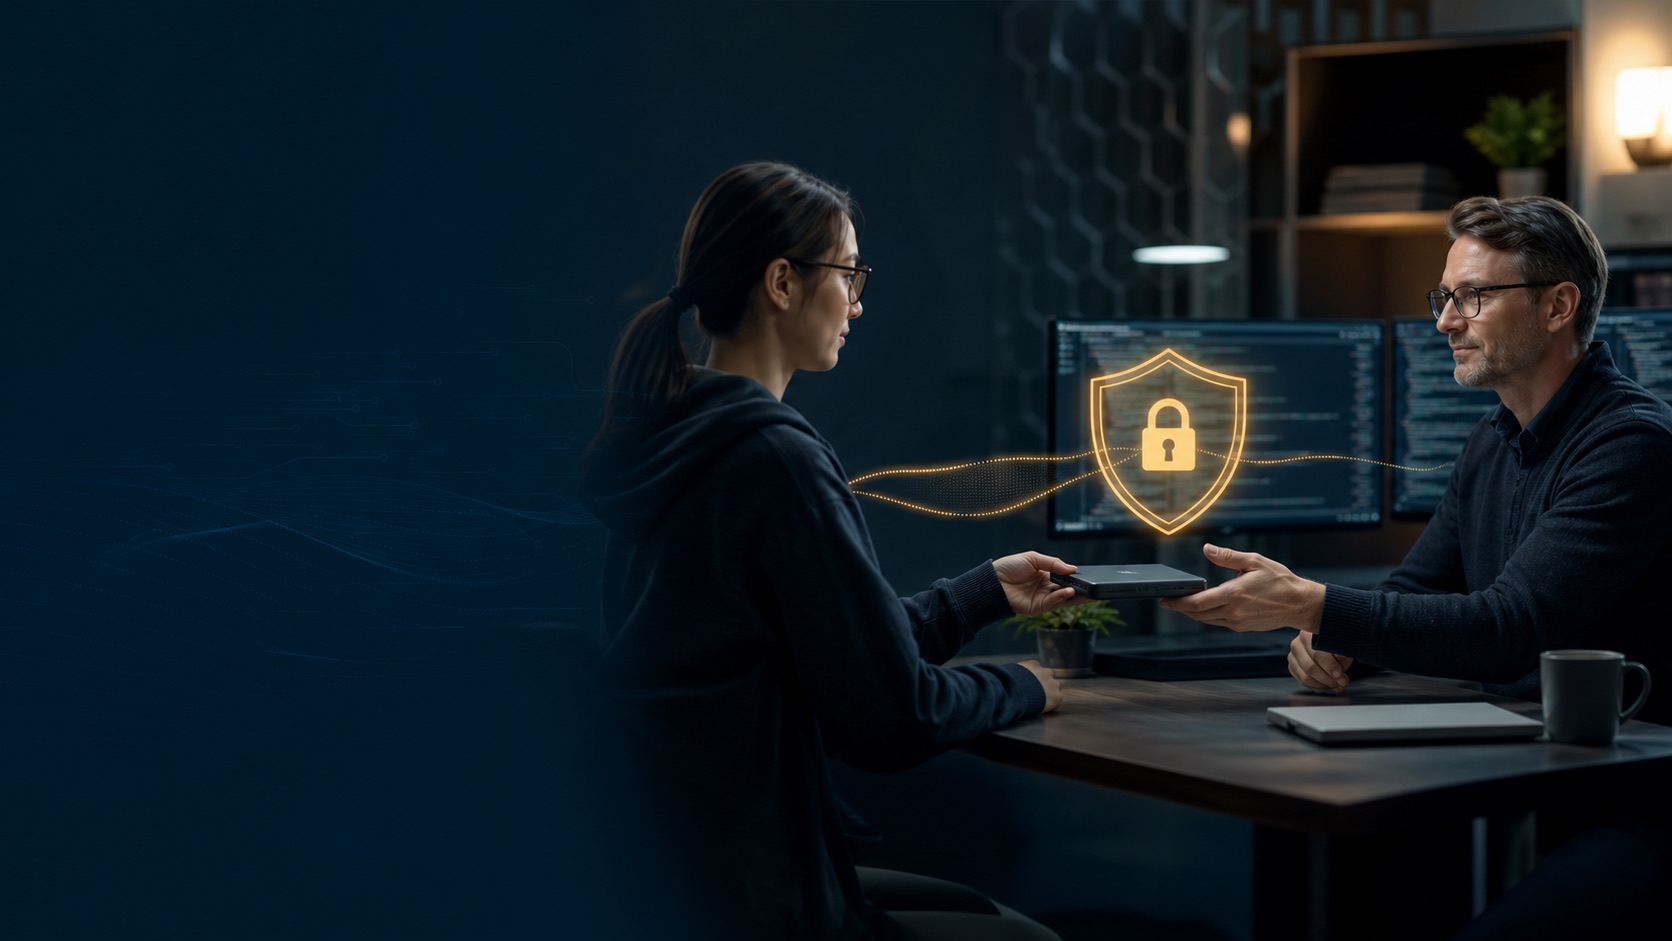
Security researcher and product response professional completing a protected vulnerability report handoff
Disclosure guidance

Review your policy

A new multi-agency cybersecurity information sheet urges organizations to establish accessible, inclusive and well-governed coordinated vulnerability disclosure programs.

At a glance

  • The guidance was developed by NSA, CISA, JPCERT/CC, the Netherlands' NCSC and other partners.
  • Organizations are encouraged to publish a vulnerability disclosure policy and provide a clear public reporting channel.
  • The recommendations support broad security-testing scope and the use of trusted intermediaries where appropriate.
  • Disclosure programs should be maintained and updated rather than treated as a one-time policy document.

Copyright

© SecurityTalent.com — original summary and analysis

  131 Hits

Cisco Midyear Advisories Reinforce Network Device Exposure Management

Security operations team reviewing Cisco Midyear Advisories Reinforce Network Device Exposure Management
Advisory roundup

Review inventory

Cisco's 2026 advisory stream shows why organizations need current network-device inventory, supported software branches and evidence-driven upgrade processes.

At a glance

  • Cisco advisories distinguish affected releases, fixed releases, workarounds and exploitation status.
  • Teams should subscribe to PSIRT notifications and map each bulletin to an accountable device owner.

Copyright

© SecurityTalent.com — original summary and analysis

  70 Hits

Secure Boot Certificate Expiry Requires Windows and Linux VM Readiness Checks

Security operations team reviewing Secure Boot Certificate Expiry Requires Windows and Linux VM Readiness Checks
Platform resilience

Validate certificate updates

Google Cloud reminded customers that 2011 Secure Boot certificates begin expiring in June 2026 and systems without the 2023 certificates may miss future early-boot protections.

At a glance

  • Existing systems should continue to start, but new boot protections and revocation updates may fail without refreshed certificates.
  • The issue affects Windows and some Linux Secure Boot workflows.

Copyright

© SecurityTalent.com — original summary and analysis

  77 Hits
